

 Saudi Arabia
 UAE
 Qatar
 Bahrain
 Kuwait
 Oman
 Lebanon
 Egypt
 India
 UK
 Ireland
 Germany
 USA
 Australia
 Singapore
 South Africa
 Iraq
 Jordan
 Hungary
 Georgia
 Turkey
 LagosNigeria


 SIEM · UAE
ManageEngine Log360 SIEM Implementation in the UAE
ManageEngine Log360 UAE projects from Shyphan give your security team a working SIEM: logs from firewalls, servers, Active Directory, databases and Microsoft 365 in one place, with correlation rules, behaviour analytics and compliance reports. We size storage, onboard log sources in priority order, tune rules to cut noise and hand over incident workflows your team can run.
Prefer to talk? Call +971 55 145 3265
Get a free recommendation
Tell us what you want to fix. A senior consultant replies within one working day with a written view.
Trusted by businesses across the UAE, Saudi Arabia and beyond
ManageEngine Log360 SIEM Implementation in the UAE: the short answer
- What it is
- Log360 is ManageEngine's SIEM, collecting and correlating logs, adding user and entity behaviour analytics (UEBA) and threat intelligence, and producing compliance reports.
- Best suited to
- UAE organisations that need central logging and threat detection without a large SOC: mid-size financial firms, hospitals, schools, government-linked entities and companies audited against ISO 27001.
- Core stack
- ManageEngine Log360, EventLog Analyzer, ADAudit Plus, Microsoft 365, FortiGate or Palo Alto firewalls, ServiceDesk Plus
- Typical timeline
- Four to sixteen weeks depending on the platform, modules, data migration and integrations; we phase larger programmes.
- What it costs
- A fixed price in AED after a free discovery call, phased so you are never committing to the whole programme on day one. Platform licences are billed by the vendor.
- Local specifics
- UAE IA Regulation logging; Logs stay in the UAE; PDPL breach readiness.
- Delivered by
- Shyphan AI Solutions: Zoho Premium Partner, Official Odoo Partner, independent Dynamics 365 consultancy and custom software house, so the platform is chosen by fit.
- Last reviewed
- 29 September 2026
ManageEngine Log360 SIEM Implementation in the UAE: who it is for
UAE organisations that need central logging and threat detection without a large SOC: mid-size financial firms, hospitals, schools, government-linked entities and companies audited against ISO 27001. Log360 is ManageEngine's SIEM, collecting and correlating logs, adding user and entity behaviour analytics (UEBA) and threat intelligence, and producing compliance reports.
- Priority log onboarding
- Correlation rules that fit
- UEBA baselines
- Threat intelligence feeds
What we use to deliver manageengine log360 SIEM implementation
Tools and platforms we typically use, and the systems it connects to. The final choice is made against your systems, budget and team.
 Odoo
 Business Central
 Microsoft 365
 WhatsApp
ManageEngine Log360 SIEM Implementation in the UAE: what is included
ManageEngine Log360 UAE projects from Shyphan give your security team a working SIEM: logs from firewalls, servers, Active Directory, databases and Microsoft 365 in one place, with correlation rules, behaviour analytics and compliance reports.
Priority log onboarding
We onboard sources in the order that gives the most visibility first: domain controllers, firewalls, VPN, Microsoft 365, critical servers, then databases and applications, checking parsing on each. Sources that fail to parse are fixed with custom parsers.
Correlation rules that fit
We start from built-in correlation rules for brute force, lateral movement and privilege abuse, then disable or tune the ones that fire on normal behaviour in your network so analysts trust the alerts.
UEBA baselines
User and entity behaviour analytics learn normal logon times, hosts and data volumes, then score anomalies such as an HR user suddenly reading finance shares at night. Risk scores add up per user, so analysts focus on the few people behaving oddly.
Threat intelligence feeds
Log360 matches traffic and logons against threat intelligence feeds of known malicious IPs, domains and URLs, and flags communication with them from firewall and proxy logs. Matches raise an alert with the source device and user.
Incident workflows
Alerts create incidents with automated first steps, such as disabling an account or opening a ServiceDesk Plus ticket, and analysts follow runbooks we write with your team. Each workflow step is logged, which gives the incident timeline auditors ask for.
Compliance reporting
Ready reports for ISO 27001, PCI DSS and other frameworks are scheduled, and we add custom reports for UAE requirements your auditors raise, with archived logs kept for the retention you set.
Property manager preparing for ransomware
How manageengine log360 SIEM implementation in the UAE looks in practice. Illustrative; every project is scoped to the business.
For example, a property management company with offices in Dubai and Sharjah holds tenant contracts, ID copies and payment records on Windows file servers and Microsoft 365. A peer firm was hit by ransomware, and the board has asked its small IT team for early warning. The team is two people, and an external provider covers evenings and weekends.
- Onboard domain controllers, file servers, FortiGate firewalls and Microsoft 365 into Log360, sizing storage for the retention period agreed with the board and legal adviser.
- Enable correlation rules for ransomware precursors, such as mass file renames, new admin accounts, disabled security tools and unusual outbound traffic, tuned against a fortnight of normal activity.
- Route high-severity alerts to the in-house team during office hours and to the external provider after hours, with a shared runbook for isolating affected machines.
See it in ManageEngine Log360
Real screens from the platforms we implement. Yours are configured to your entities, processes and KPIs.
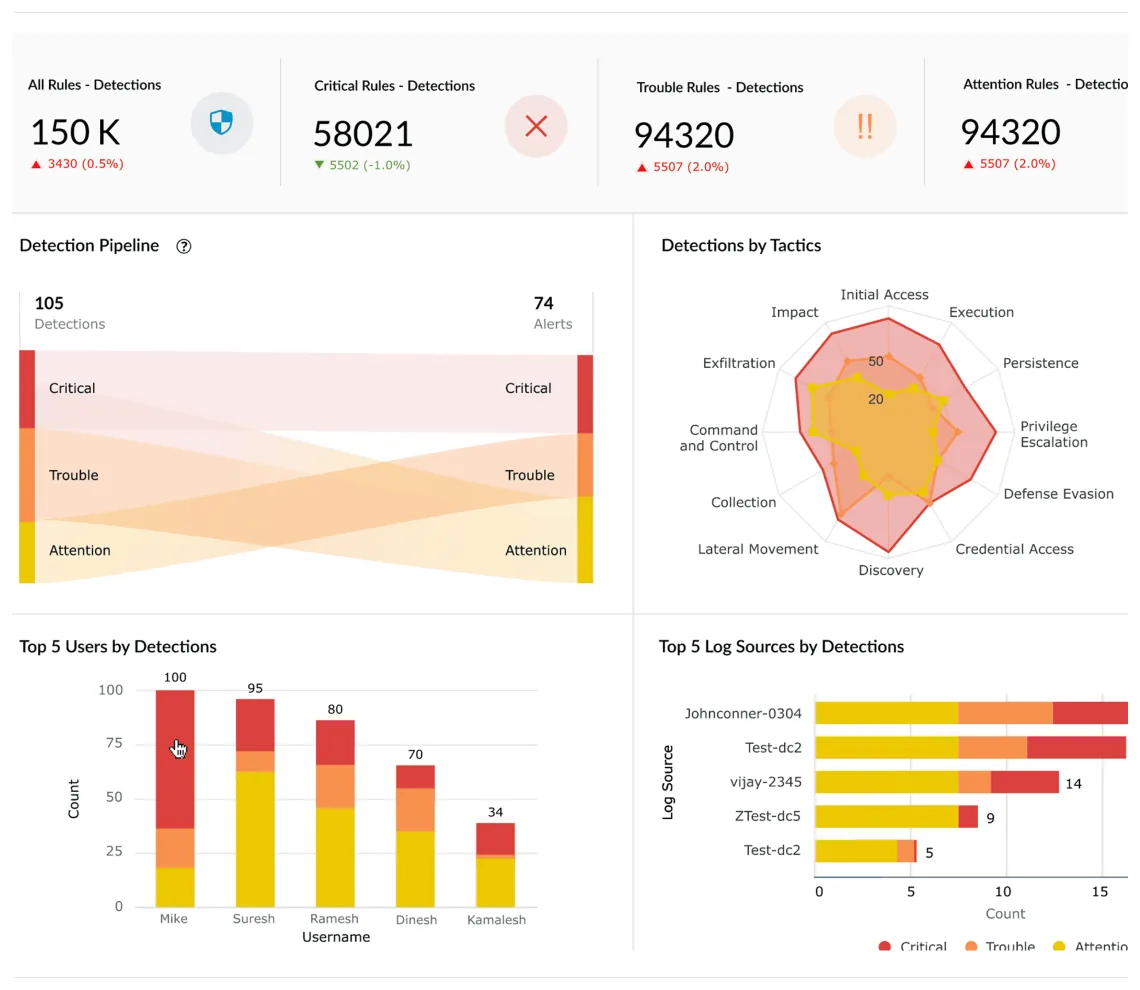
Threat detections in Log360
Critical, trouble and attention detections, a detection pipeline, detections mapped to MITRE ATT&CK tactics, and top users and log sources by detections.
- Priority log onboarding
- Correlation rules that fit
- UEBA baselines
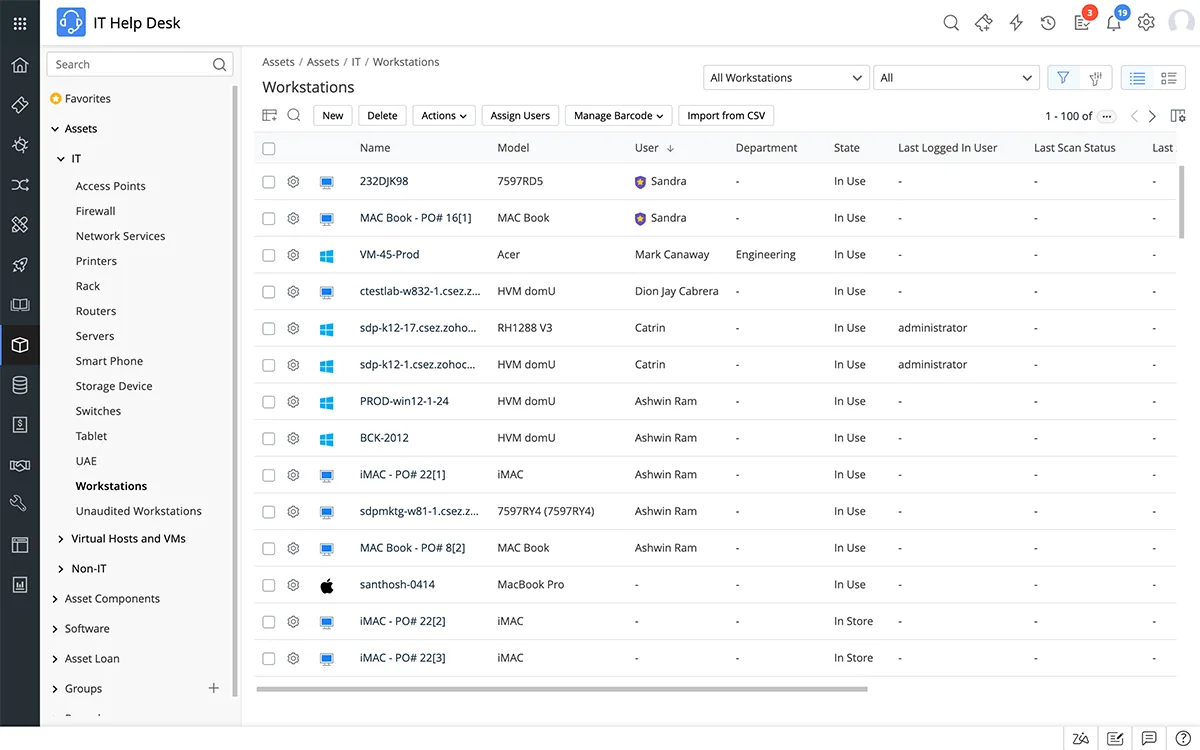
IT asset inventory in ServiceDesk Plus
Discovered workstations with model, assigned user, department, state and last scan, plus an asset tree for servers, routers, printers and virtual hosts.
- Threat intelligence feeds
- UAE IA Regulation logging
- Logs stay in the UAE
 ServiceDesk Plus
 Endpoint Central
 PAM360
 OpManager
 ADManager Plus
 Log360
Which platform for manageengine log360 SIEM implementation in the UAE?
An honest comparison. We implement all of these, so the recommendation follows your processes, team and budget.
| Option | Best when | How it fits this need |
|---|---|---|
| Log360 | A small team needs SIEM, AD auditing and ready reports together. | Brings log collection, correlation, UEBA and AD auditing into one product with packaged reports, which suits UAE mid-sized firms without dedicated security analysts. |
| EventLog Analyzer alone | Log collection and compliance reports are the main need. | ManageEngine's log management product, included within Log360. A lighter start if you do not yet need UEBA, cloud auditing and wider correlation across sources. |
| Microsoft Sentinel | Your estate is largely Azure and Microsoft 365 E5. | A capable cloud SIEM with strong Microsoft integration. Costs follow data ingestion volume, so busy firewalls and file servers need careful filtering to keep spend predictable. |
| Open-source SIEM | Security engineers can build and maintain rules themselves. | Tools such as Wazuh avoid licence costs and are flexible. They need significant engineering time for rules, dashboards and reports that commercial products provide ready-made. |
What changes in the UAE
The local rules and realities we design for before go-live. Rules change, so we re-check the current position at scoping.
UAE IA Regulation logging
Government-linked and critical-sector entities following the UAE IA Regulation need central logging, monitoring and incident handling. Log360 covers much of that technical control set; we confirm the current requirement at scoping.
Logs stay in the UAE
Log360 runs on servers you control, in your UAE data centre or on Azure UAE North or AWS me-central-1, which suits organisations that do not want security logs held abroad.
PDPL breach readiness
The UAE PDPL and the DIFC and ADGM data protection laws expect breaches to be detected and reported. Log360 gives the detection and the timeline you need to assess a breach.
What drives the cost, and what it connects to
No price list: we quote a fixed price in AED after discovery. These are the factors that move the effort up or down.
Log sources and devices
Log360 licensing reflects the devices and sources you collect from, so the number of servers, firewalls, cloud accounts and applications directly shapes the licence and onboarding effort.
Storage and retention
Daily log volume multiplied by the retention period determines storage. Longer retention for legal, audit or PDPL breach investigations needs more disk and a tested archive plan.
Rule tuning effort
Default rules generate noise in most environments. Tuning against a baseline of normal activity, and revisiting after changes, takes analyst time during and after the project.
Runbooks and training
Writing incident runbooks, practising them with the team and training an external provider adds effort, but makes the SIEM useful when an actual incident happens.
What it connects to
Traffic, VPN and threat logs flow into Log360, showing outbound connections and remote access linked to suspicious internal activity.
Sign-ins, mailbox rules, SharePoint and OneDrive activity are collected, catching account takeover and unusual data sharing in the cloud.
File changes, renames and permission edits are audited, supporting early detection of mass encryption and data theft attempts.
Confirmed alerts create incident tickets with evidence attached, and closure notes feed monthly security reporting.
After-hours alerts are forwarded by email, SMS or ticket to the provider, following the agreed escalation and isolation runbook.
How we deliver manageengine log360 SIEM implementation
Phases, indicative timing and what is delivered in each. Scope is fixed and priced in AED before we start.
Use cases and sizing
Agree threats to detect, log sources, retention and events per second to size servers and storage.
Core deployment
Install Log360, onboard domain controllers, firewalls and Microsoft 365, and verify parsing. Confirm event rates match the sizing estimate.
Extend sources
Add servers, databases, applications and cloud; enable UEBA and threat feeds. Add custom parsers for any in-house applications.
Tune and respond
Tune correlation rules, build incident workflows and ServiceDesk Plus integration; run test attacks. Review false positives with analysts.
Handover
Train analysts, deliver runbooks and optional monthly tuning reviews. Train analysts, deliver runbooks and agree optional monthly tuning reviews with your security lead.
When manageengine log360 SIEM implementation is the wrong answer
A SIEM needs someone to look at it. If you have no analyst time at all, Log360 alerts will pile up unread; a managed detection service may be a better fit, and we will say so. For a small office whose only need is AD auditing, ADAudit Plus alone is cheaper.
How we handle it: We implement Zoho, Odoo and Dynamics 365 and build AI and custom software, so our written recommendation can point you to a simpler option, or to doing nothing yet.
Checklist and common mistakes
Buyer's checklist
What to ask for before you choose a provider.
- Ask the provider which log sources they will onboard first and how they chose that order for your risks.
- Require a storage sizing estimate based on your actual daily log volumes, not a generic rule of thumb.
- Check how correlation rules will be tuned against your normal activity before alerts go to people.
- Ask how after-hours alerts will reach someone who can act, whether in-house or an external provider.
- Confirm a written runbook for the most likely incidents, such as ransomware and compromised accounts.
- Request a quarterly tuning review in the support plan, because alert rules drift as your systems change.
Common mistakes
What we see go wrong in the UAE, and how to avoid it.
- Collecting everything with no planSending every log from day one fills storage and buries real alerts. Onboard sources by risk, confirm each is useful, then add the next group.
- Nobody watching after hoursAttacks often start in the evening or at weekends. Arrange an on-call person or external provider for high-severity alerts before relying on the SIEM.
- Leaving default rules untunedUntuned rules produce so many alerts that staff stop reading them. Baseline normal activity, tune thresholds, then review rules again every quarter.
- No incident runbookA SIEM tells you something is wrong but not what to do. Write and rehearse short runbooks for ransomware, account takeover and data leaks.
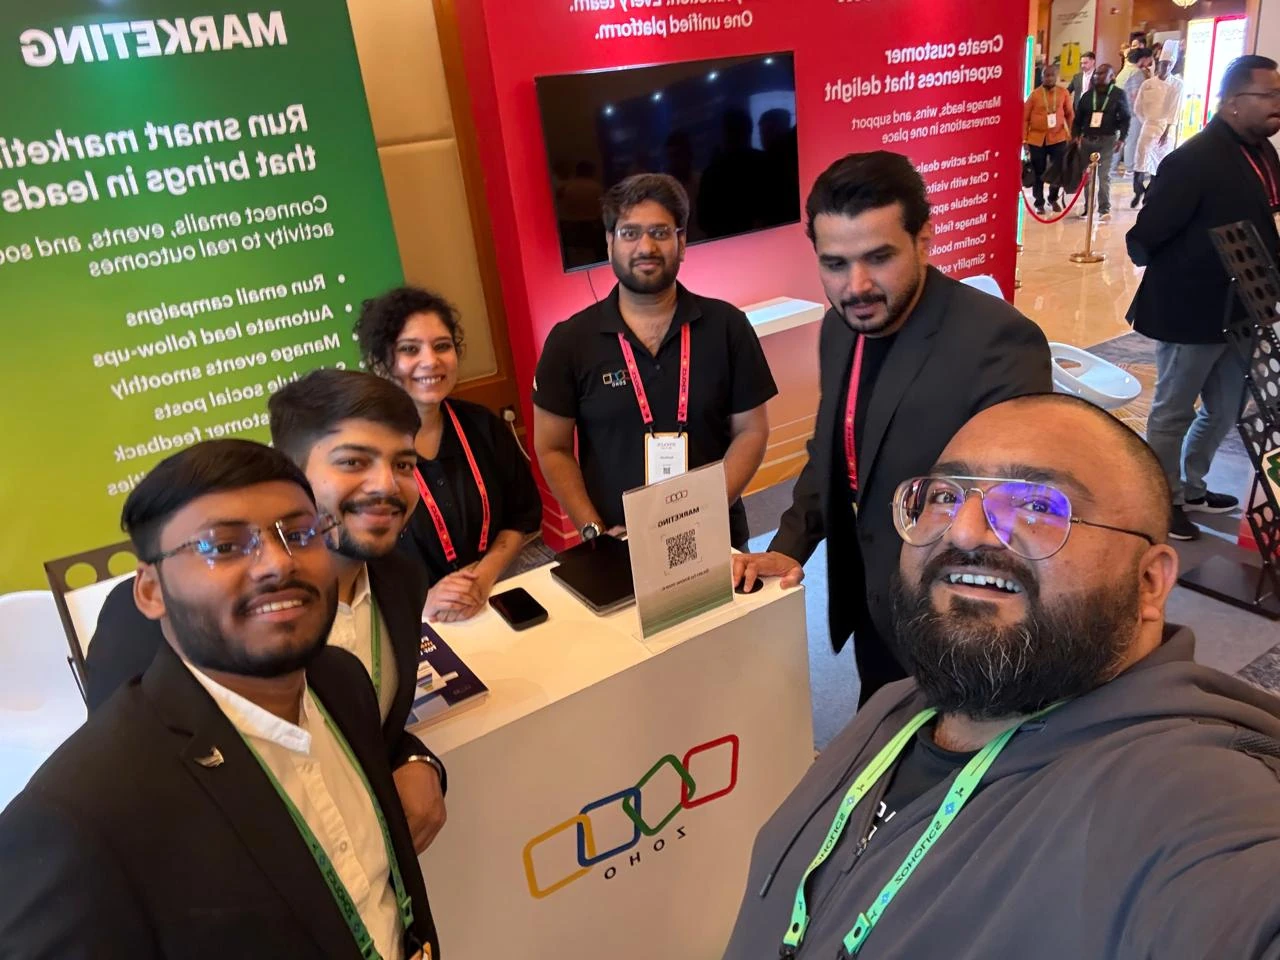
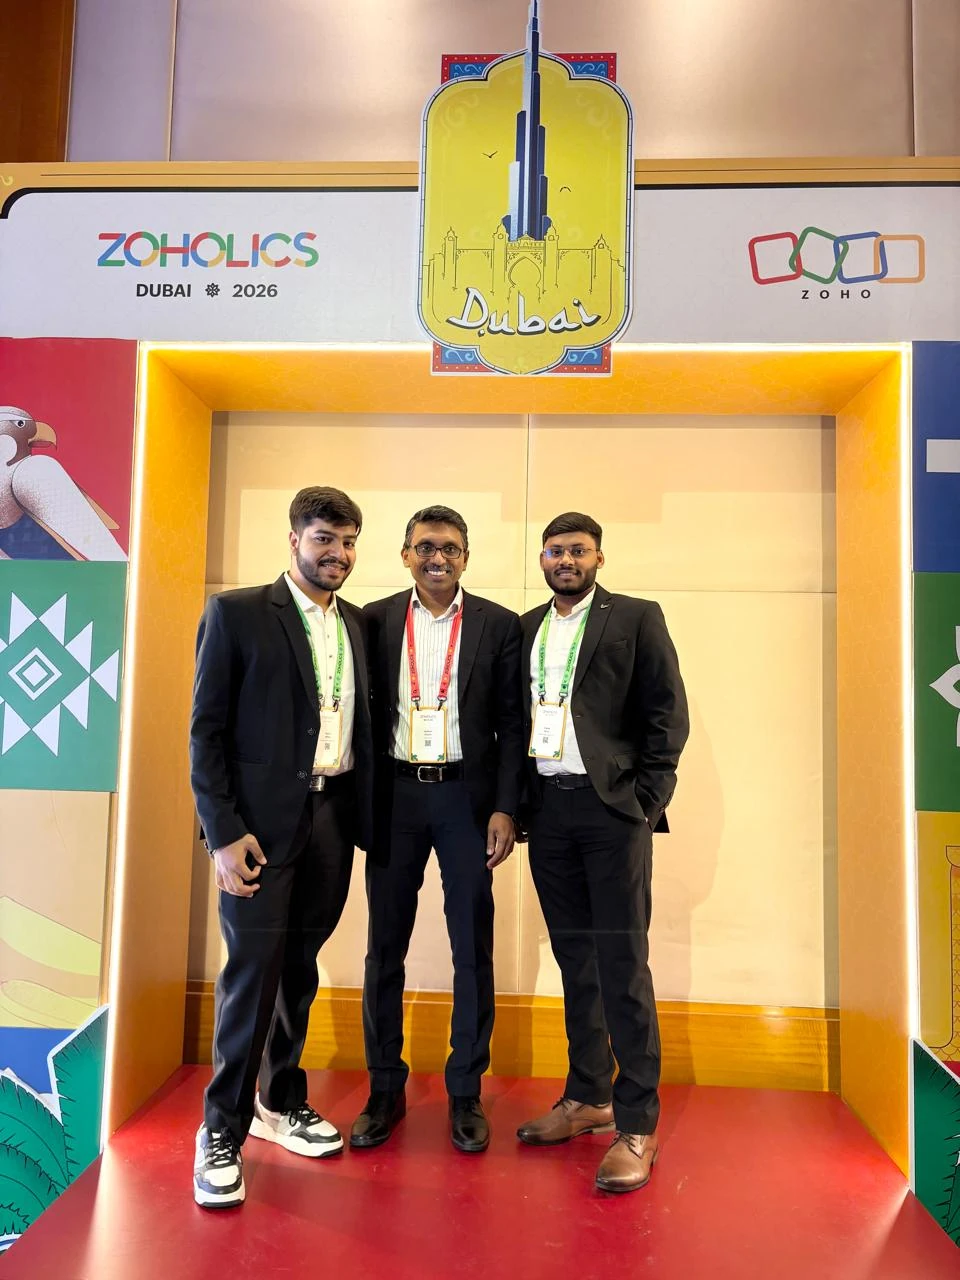
A UAE team you can meet in person
That is our team at Zoholics Dubai 2026. We deliver Zoho, Odoo, Dynamics 365 and custom projects from our Ras Al Khaimah office with remote delivery across all seven emirates, in English and Arabic, and we run workshops on site in Dubai, Abu Dhabi and Sharjah when a project needs it.
ManageEngine Log360 SIEM Implementation in the UAE: questions we get asked
What does ManageEngine Log360 UAE implementation include?
How is Log360 different from ADAudit Plus?
Can Log360 collect Microsoft 365 and Azure logs?
How much storage will we need?
Will Log360 help with UAE IA Regulation audits?
Can you tune Log360 after go-live?
Can Log360 give a UAE company early warning of ransomware?
Can a two-person IT team in the UAE run Log360?
How long should a UAE business keep security logs in Log360?
Why choose Shyphan?
Talk to a consultant about manageengine log360 SIEM implementation
A free 30-minute call, then a written recommendation and a fixed quote in AED, including the honest option that this is not the right fit.