

 Saudi Arabia
 UAE
 Qatar
 Bahrain
 Kuwait
 Oman
 Lebanon
 Egypt
 India
 UK
 Ireland
 Germany
 USA
 Australia
 Singapore
 South Africa
 Iraq
 Jordan
 Hungary
 Georgia
 Turkey
 LagosNigeria


 SIEM · Abu Dhabi
ManageEngine Log360 in Abu Dhabi
ManageEngine Log360 in Abu Dhabi for organisations that need central logging and threat detection but do not run a large security operations centre. Shyphan deploys Log360 for government-linked entities, ADGM financial firms, hospitals and energy companies, onboards logs by priority, tunes correlation and UEBA, keeps data on UAE servers and builds the monitoring evidence that IA Regulation assessors ask to see.
Prefer to talk? Call +971 55 145 3265
Get a free recommendation
Tell us what you want to fix. A senior consultant replies within one working day with a written view.
Trusted by businesses across the UAE, Saudi Arabia and beyond
ManageEngine Log360 in Abu Dhabi: the short answer
- What it is
- Log360 is ManageEngine's SIEM, collecting and correlating logs, adding user and entity behaviour analytics (UEBA) and threat intelligence, and producing compliance reports.
- Best suited to
- Abu Dhabi entities with a small security team or an outsourced SOC, organisations assessed under the UAE IA Regulation, and ADGM firms that must detect and document incidents.
- Core stack
- Log360, EventLog Analyzer, ADAudit Plus, FortiGate or Palo Alto firewalls, Microsoft 365, ServiceDesk Plus
- Typical timeline
- Four to sixteen weeks depending on the platform, modules, data migration and integrations; we phase larger programmes.
- What it costs
- A fixed price in AED after a free discovery call, phased so you are never committing to the whole programme on day one. Platform licences are billed by the vendor.
- Local specifics
- UAE IA Regulation monitoring; ADGM data protection; IT and OT separation.
- Delivered by
- Shyphan AI Solutions: Zoho Premium Partner, Official Odoo Partner, independent Dynamics 365 consultancy and custom software house, so the platform is chosen by fit.
- Last reviewed
- 29 September 2026
ManageEngine Log360 in Abu Dhabi: who it is for
Abu Dhabi entities with a small security team or an outsourced SOC, organisations assessed under the UAE IA Regulation, and ADGM firms that must detect and document incidents. Log360 is ManageEngine's SIEM, collecting and correlating logs, adding user and entity behaviour analytics (UEBA) and threat intelligence, and producing compliance reports.
- Monitoring evidence for IA reviews
- SOC-lite for small security teams
- Working with an outsourced SOC
- Energy and utility IT logs
What we use to deliver manageengine log360
Tools and platforms we typically use, and the systems it connects to. The final choice is made against your systems, budget and team.
 Odoo
 Business Central
 Microsoft 365
 WhatsApp
ManageEngine Log360 in Abu Dhabi: what is included
ManageEngine Log360 in Abu Dhabi for organisations that need central logging and threat detection but do not run a large security operations centre.
Monitoring evidence for IA reviews
We configure log sources, retention, correlation rules and reports to match the monitoring and incident management areas Abu Dhabi entities are assessed on under the UAE IA Regulation. Evidence is produced from the system itself. We confirm the current requirement at scoping.
SOC-lite for small security teams
Many Abu Dhabi entities have two or three security staff. We tune rules so they see a short daily list of real alerts, automate first responses such as disabling an account, and set a weekly review routine they can sustain.
Working with an outsourced SOC
If a managed security provider watches your alerts, we configure Log360 so they get the right access and alert feed while logs stay on your UAE servers and your own team keeps control of retention and reports.
Energy and utility IT logs
For energy and utility firms we collect logs from corporate IT, remote access gateways and IT-side jump servers used by vendors. OT event sources are added only with the OT owner's approval and through the gateways they choose.
ADGM incident readiness
ADGM firms need to establish quickly what happened in a suspected breach. We prepare investigation dashboards and saved searches for logons, data access and privilege changes so the facts are ready when compliance asks.
Retention on UAE storage
Logs, archives and indexes stay on servers you control in the UAE. We size storage from real event rates and set hot and archive retention to what your policy and regulators require.
Private hospital watching EHR and email
How manageengine log360 in Abu Dhabi looks in practice. Illustrative; every project is scoped to the business.
Picture a private hospital in Abu Dhabi with an electronic health record system, Microsoft 365 email, and a medical device network managed by biomedical engineering. Staff receive convincing phishing emails, a shared nursing workstation account keeps appearing in odd places, and the IT security officer has no single view of sign-ins, email threats and access to patient records.
- Onboard Microsoft 365, Active Directory, firewall and EHR application logs into Log360 first, leaving medical device networks to a later, separately planned phase with biomedical engineering.
- Build alerts for suspicious sign-ins after phishing clicks, bulk patient record access and shared account use from unusual workstations, routed to the security officer.
- Create a monthly report for the hospital's information governance committee covering access anomalies, phishing outcomes and incidents handled.
See it in ManageEngine Log360
Real screens from the platforms we implement. Yours are configured to your entities, processes and KPIs.
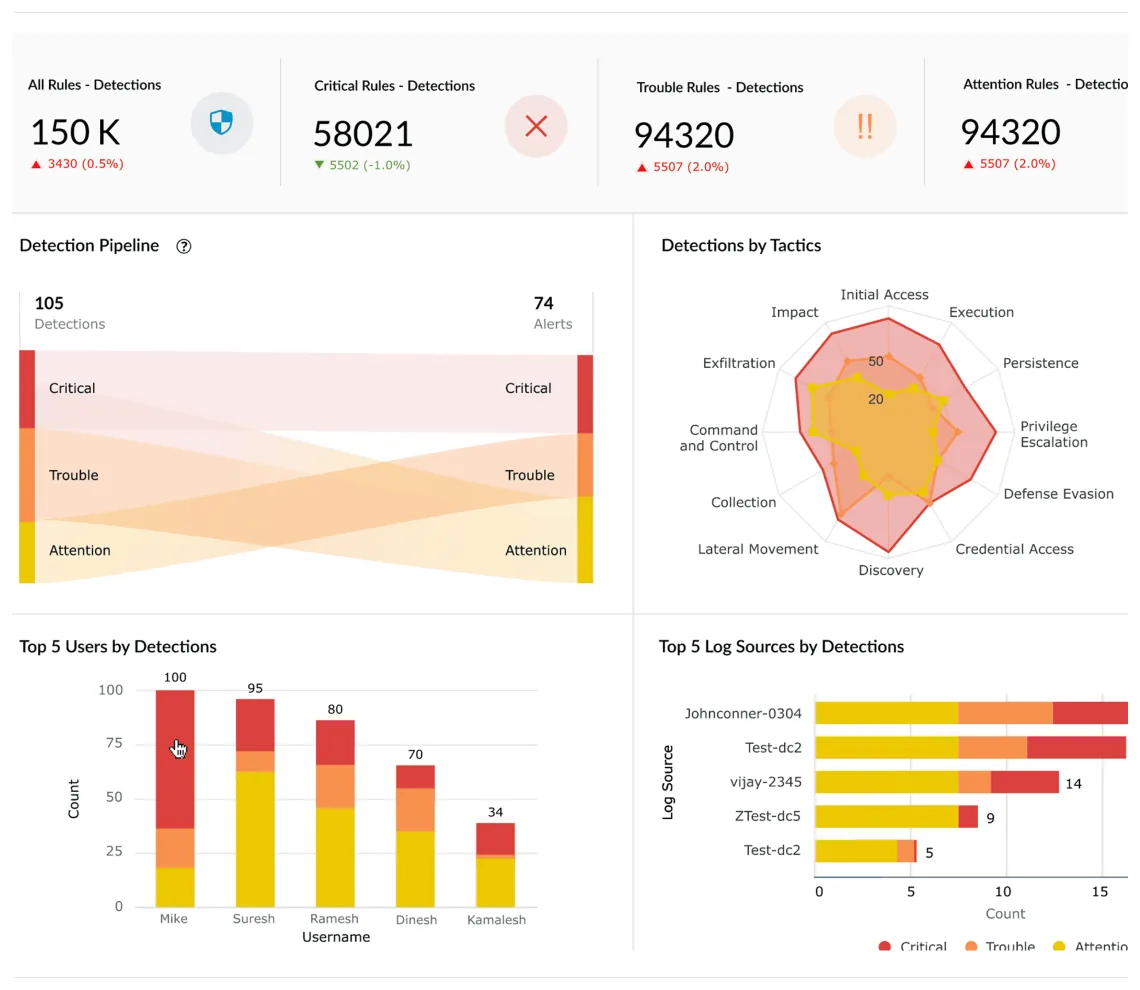
Threat detections in Log360
Critical, trouble and attention detections, a detection pipeline, detections mapped to MITRE ATT&CK tactics, and top users and log sources by detections.
- Monitoring evidence for IA reviews
- SOC-lite for small security teams
- Working with an outsourced SOC
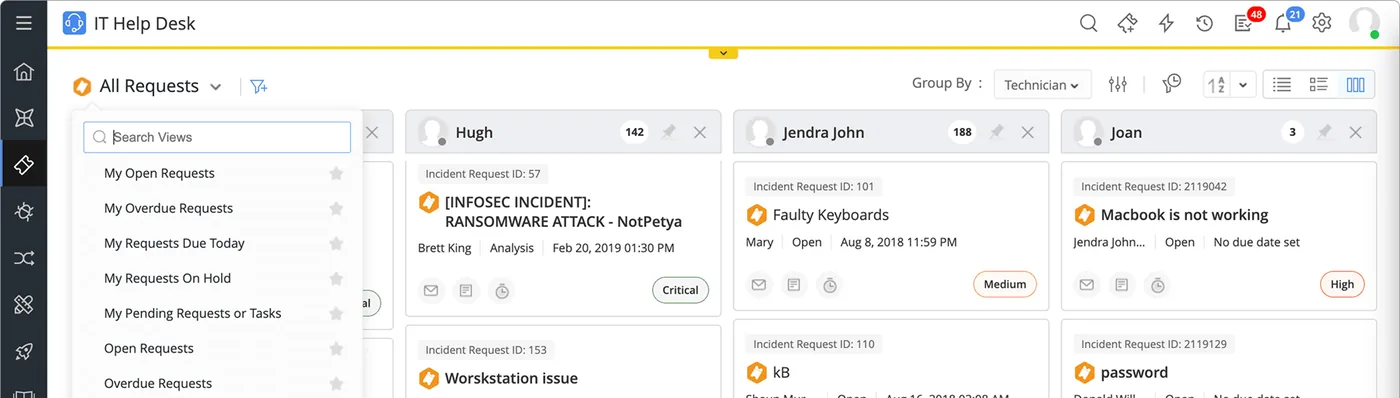
Incident requests in ServiceDesk Plus
The IT help desk request board grouped by technician, with incident IDs such as a ransomware alert and faulty keyboards, status and priority tags.
- Energy and utility IT logs
- UAE IA Regulation monitoring
- ADGM data protection
 ServiceDesk Plus
 Endpoint Central
 PAM360
 OpManager
 ADManager Plus
 Log360
Which platform for manageengine log360 in Abu Dhabi?
An honest comparison. We implement all of these, so the recommendation follows your processes, team and budget.
| Option | Best when | How it fits this need |
|---|---|---|
| Log360 | One security officer or a small team needs SIEM and AD auditing together. | Combines log management, AD auditing and correlation with ready reports. Suits Abu Dhabi hospitals and mid-sized organisations without a full security operations centre. |
| Microsoft Sentinel | Microsoft 365 E5 and Azure are central to the estate. | A strong cloud SIEM for Microsoft-heavy estates. Costs depend on ingested data volume, and on-premises sources such as EHR servers need connectors and careful planning. |
| Managed SOC service | No internal staff can watch alerts outside working hours. | Gives round-the-clock monitoring by an external team. You still need clear log sources and escalation rules, and Log360 can be the platform they watch. |
| EHR vendor audit logs only | Record access is the only concern. | The EHR's own audit trail is essential, but it does not see email, sign-ins or network threats. Correlating those needs a SIEM alongside it. |
What changes in Abu Dhabi
The local rules and realities we design for before go-live. Rules change, so we re-check the current position at scoping.
UAE IA Regulation monitoring
Central logging and monitoring are common audit areas for government-linked and critical-sector entities in Abu Dhabi. Log360 provides the logs, alerts and reports; we confirm the current requirement at scoping.
ADGM data protection
ADGM-licensed firms operate under the ADGM data protection regulations. Logs contain personal data, so we set viewer permissions, retention and masking where needed and keep everything on UAE infrastructure.
IT and OT separation
Energy and utility companies keep OT networks separate. We collect from the IT side and approved gateways only, and agree with OT owners exactly what crosses the boundary.
Working with businesses in Abu Dhabi: we support companies across ADGM, KIZAD, Musaffah and Masdar City, with remote delivery and on-site workshops where the project needs them.
What drives the cost, and what it connects to
No price list: we quote a fixed price in AED after discovery. These are the factors that move the effort up or down.
Log sources and volume
Log360 is licensed partly by log sources and devices, and busy sources such as firewalls and Microsoft 365 generate large volumes that shape storage and licence needs.
Clinical application logs
EHR and clinical systems often need custom log parsing and careful testing, which takes more effort than standard Windows or firewall sources.
Alert tuning
Hospitals have unusual but legitimate access patterns. Tuning alerts to avoid false alarms during rounds, shift changes and emergencies takes time with clinical staff.
Retention and storage
Longer retention for security investigations and hospital governance needs more storage, archive and restore planning, especially when logs must remain on UAE-hosted infrastructure.
What it connects to
Sign-in, mailbox and email threat events flow into Log360, linking phishing clicks with suspicious account activity afterwards.
Patient record access logs are parsed and correlated with user sign-ins and workstation locations for anomaly alerts.
Account changes, lockouts and shared account use are audited and correlated with other security events.
Perimeter traffic and blocked connections flow in, showing outbound connections from devices after suspicious activity.
Confirmed security alerts raise incident tickets, tracking investigation and closure for governance reporting.
How we deliver manageengine log360
Phases, indicative timing and what is delivered in each. Scope is fixed and priced in AED before we start.
Source inventory
Log sources listed and ranked: domain controllers, firewalls, VPN, Microsoft 365, critical servers, then applications and databases.
Sizing and build
Event rates measured, storage sized, Log360 deployed on UAE servers and connected to Active Directory.
Onboard by priority
Sources added in priority order with parsing checked on each, and custom parsers built where needed.
Tune and automate
Correlation rules and UEBA baselines tuned to your normal behaviour, and first-response workflows automated and tested.
Evidence and handover
Report pack reviewed with your compliance team, and analysts trained on triage, investigation and monthly reporting.
When manageengine log360 is the wrong answer
If your Abu Dhabi organisation already has a mature SIEM run by a 24/7 SOC, replacing it with Log360 rarely pays off. We would instead look at whether ADAudit Plus or EventLog Analyzer can fill a specific reporting gap alongside your existing platform.
How we handle it: We implement Zoho, Odoo and Dynamics 365 and build AI and custom software, so our written recommendation can point you to a simpler option, or to doing nothing yet.
Checklist and common mistakes
Buyer's checklist
What to ask for before you choose a provider.
- Ask which log sources the provider will onboard first and why, starting with email, identity and patient data systems.
- Require a separate, carefully planned approach for medical device networks, agreed with biomedical engineering.
- Check how alerts on patient record access will be tuned to avoid flagging normal clinical workflows.
- Ask how the design supports DOH-related and PDPL expectations; we confirm current requirements at scoping.
- Confirm storage sizing, retention period and whether logs stay on UAE-hosted servers.
- Request a monthly governance report template that non-technical committee members can understand.
Common mistakes
What we see go wrong in the UAE, and how to avoid it.
- Onboarding medical devices too earlyConnecting medical device networks without biomedical engineering can disrupt care. Treat them as a separate phase with vendor guidance and careful testing.
- Alerting on normal clinical accessClinicians legitimately open many patient records during ward rounds. Tune alerts with clinical input so real anomalies stand out from normal care.
- Ignoring shared workstation accountsShared accounts hide who actually did what on a workstation. Plan named logons or fast user switching alongside the SIEM, or investigations will stall.
- Reports only IT understandsGovernance committees need plain, short summaries they can act on. Build a monthly report in business language as well as technical dashboards for the security team.
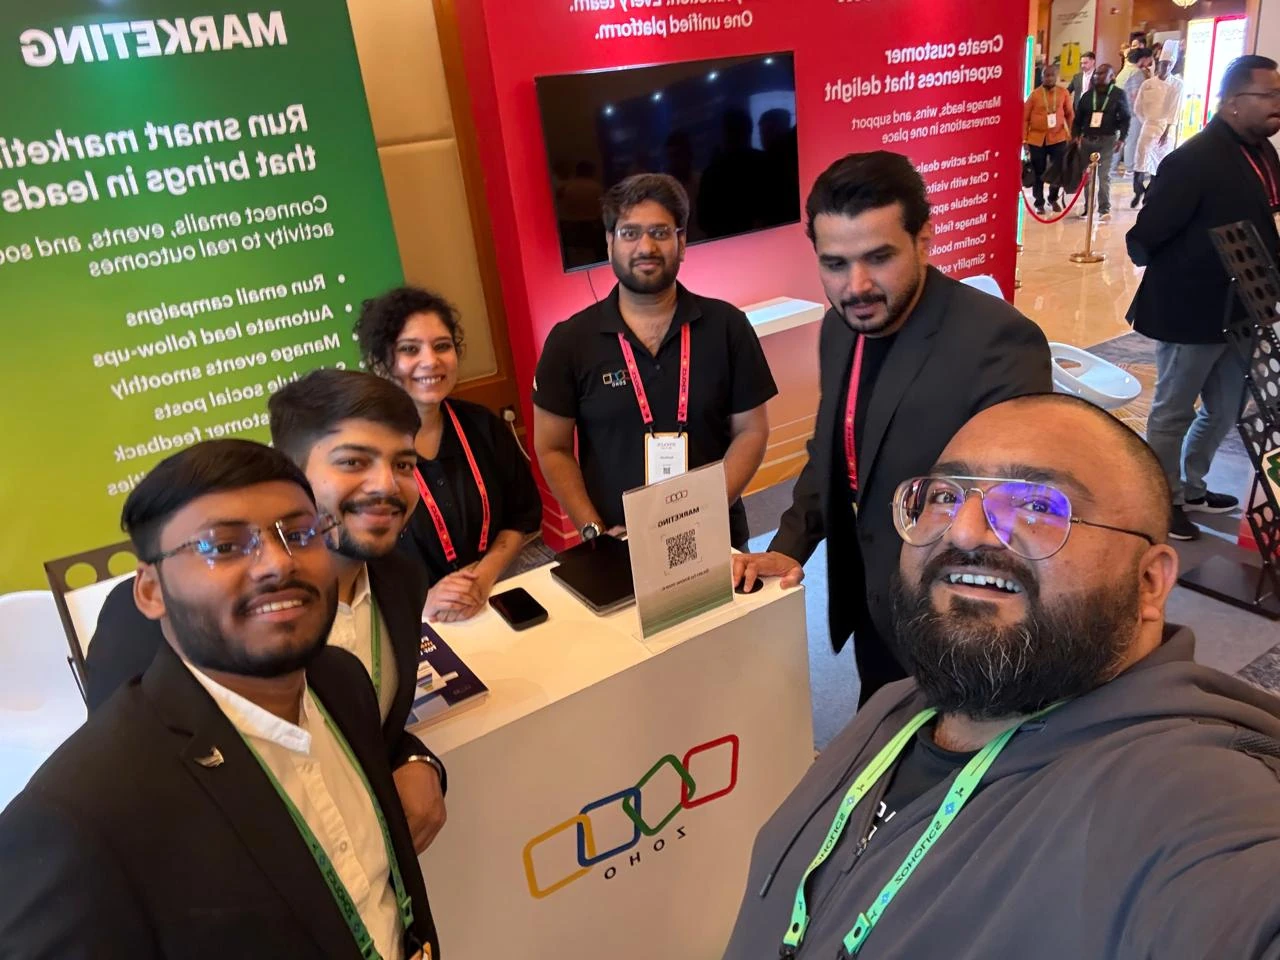
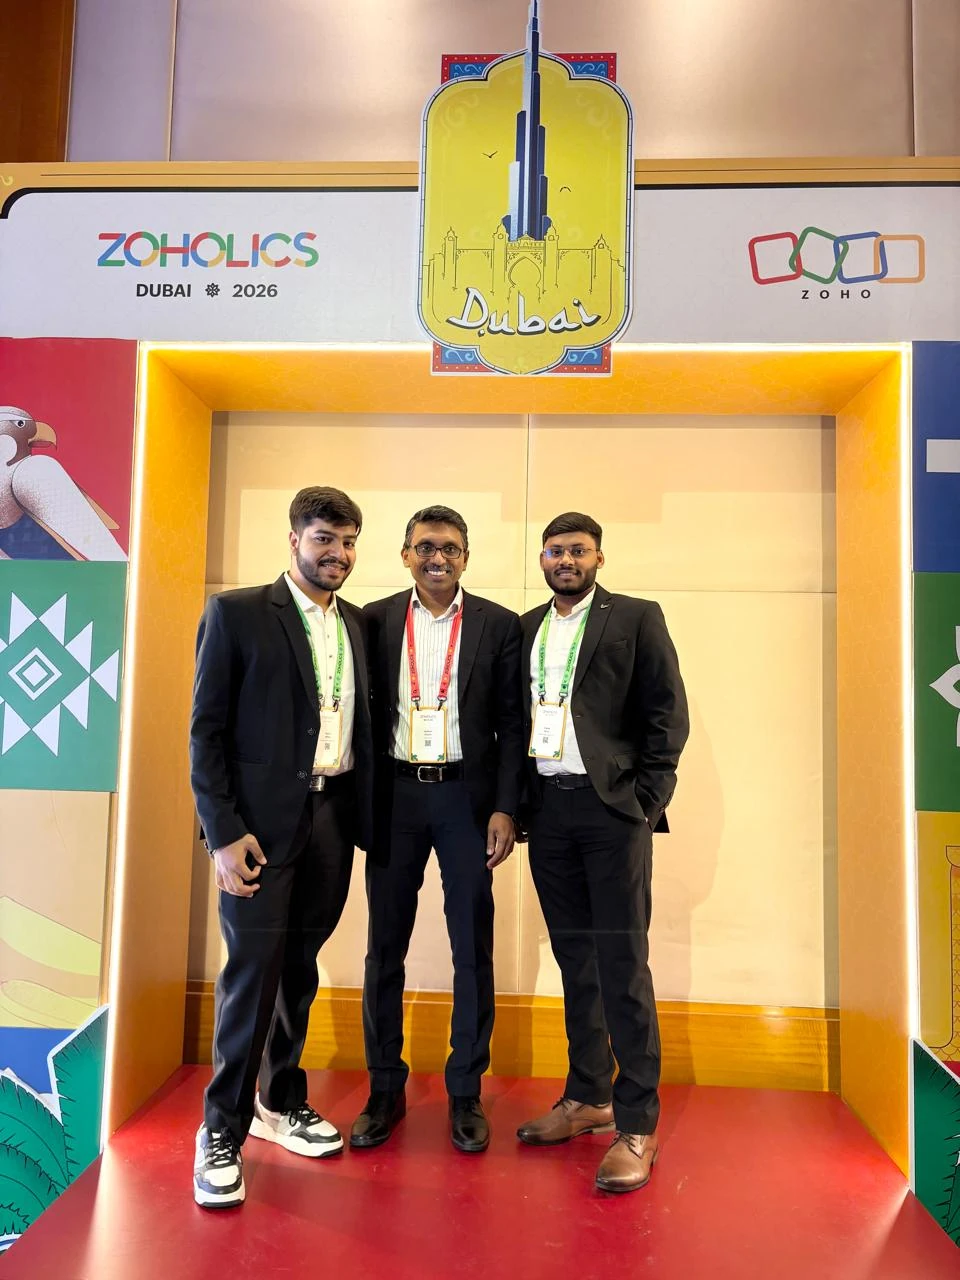
A UAE team you can meet in person
That is our team at Zoholics Dubai 2026. We deliver Zoho, Odoo, Dynamics 365 and custom projects from our Ras Al Khaimah office with remote delivery across all seven emirates, in English and Arabic, and we run workshops on site in Dubai, Abu Dhabi and Sharjah when a project needs it.
ManageEngine Log360 in Abu Dhabi: questions we get asked
What does a ManageEngine Log360 Abu Dhabi deployment include?
Can Log360 support UAE IA Regulation monitoring requirements?
We have only two security analysts. Is Log360 manageable?
Can an outsourced SOC use our Log360?
How is Log360 different from ADAudit Plus?
Is this different from your UAE Log360 page?
Can Log360 monitor access to patient records in an Abu Dhabi hospital?
Should Log360 collect logs from medical devices?
Can Log360 help detect phishing attacks against hospital staff?
Why choose Shyphan?
Talk to a consultant about manageengine log360
A free 30-minute call, then a written recommendation and a fixed quote in AED, including the honest option that this is not the right fit.