

 Saudi Arabia
 UAE
 Qatar
 Bahrain
 Kuwait
 Oman
 Lebanon
 Egypt
 India
 UK
 Ireland
 Germany
 USA
 Australia
 Singapore
 South Africa
 Iraq
 Jordan
 Hungary
 Georgia
 Turkey
 LagosNigeria


 AD change auditing · UAE
ManageEngine ADAudit Plus Implementation in the UAE
ManageEngine ADAudit Plus UAE projects from Shyphan show who changed what in Active Directory, on file servers and on Windows servers, and when. We plan audit policies so the right events are captured, deploy and size the database, build alerts for risky changes, and set up reports your auditors and data protection officer can use without asking IT for logs.
Prefer to talk? Call +971 55 145 3265
Get a free recommendation
Tell us what you want to fix. A senior consultant replies within one working day with a written view.
Trusted by businesses across the UAE, Saudi Arabia and beyond
ManageEngine ADAudit Plus Implementation in the UAE: the short answer
- What it is
- ADAudit Plus is ManageEngine's auditing tool for Active Directory, Azure AD/Entra ID, file servers and Windows servers, turning event logs into readable reports and real-time alerts.
- Best suited to
- UAE organisations facing audits or handling personal data on file shares: financial firms, healthcare providers, schools, government-linked entities and companies preparing for ISO 27001.
- Core stack
- ManageEngine ADAudit Plus, Active Directory, Windows file servers, Microsoft Entra ID, Log360, ServiceDesk Plus
- Typical timeline
- Four to sixteen weeks depending on the platform, modules, data migration and integrations; we phase larger programmes.
- What it costs
- A fixed price in AED after a free discovery call, phased so you are never committing to the whole programme on day one. Platform licences are billed by the vendor.
- Local specifics
- PDPL, DIFC and ADGM evidence; IA Regulation for critical sectors; Logs retained in the UAE.
- Delivered by
- Shyphan AI Solutions: Zoho Premium Partner, Official Odoo Partner, independent Dynamics 365 consultancy and custom software house, so the platform is chosen by fit.
- Last reviewed
- 29 September 2026
ManageEngine ADAudit Plus Implementation in the UAE: who it is for
UAE organisations facing audits or handling personal data on file shares: financial firms, healthcare providers, schools, government-linked entities and companies preparing for ISO 27001. ADAudit Plus is ManageEngine's auditing tool for Active Directory, Azure AD/Entra ID, file servers and Windows servers, turning event logs into readable reports and real-time alerts.
- AD change history
- File server access auditing
- Logon and lockout analysis
- Alerts for risky changes
What we use to deliver manageengine adaudit plus implementation
Tools and platforms we typically use, and the systems it connects to. The final choice is made against your systems, budget and team.
 Odoo
 Business Central
 Microsoft 365
 WhatsApp
ManageEngine ADAudit Plus Implementation in the UAE: what is included
ManageEngine ADAudit Plus UAE projects from Shyphan show who changed what in Active Directory, on file servers and on Windows servers, and when.
AD change history
Every change to users, groups, GPOs and OUs is shown with before and after values, the person who made it and the source machine, so a surprise Domain Admin addition is explained in minutes.
File server access auditing
We audit who read, changed, moved or deleted files on sensitive shares such as HR, payroll and patient folders, and alert on mass deletion or renaming patterns that often signal ransomware.
Logon and lockout analysis
Logon history, failed logons and account lockout sources are traced to the machine and process, which cuts time spent chasing lockouts caused by old phone or service credentials. Reports show who logged into which server and when.
Alerts for risky changes
We set alerts for changes to privileged groups, GPOs, after-hours admin logons and disabled audit policies, routed to email or ServiceDesk Plus with a clear description. Each alert names the user, the object and the change made.
Audit policy design
Windows only logs what its audit policy allows. We configure advanced audit policies and SACLs carefully so ADAudit Plus captures what matters without overloading domain controllers. We check event log sizes and forwarding at the same time so no events are lost.
Compliance report packs
Scheduled reports are grouped by audit need, for example user access reviews, privileged activity and file access on personal data shares, and archived for the retention period you set. Auditors can be given read-only report access.
Multi-emirate retailer investigating account lockouts
How manageengine adaudit plus implementation in the UAE looks in practice. Illustrative; every project is scoped to the business.
Picture a retail group with stores in Dubai, Sharjah and Ajman and a head office in Dubai. Store managers keep getting locked out at opening time, service accounts on the POS back-office servers fail at random, and the IT team suspects a mix of old saved passwords and a possible password-guessing attempt, but cannot prove either.
- Collect logon and lockout events from all domain controllers into ADAudit Plus, and build a lockout analysis report showing the source device for each failed attempt.
- Set alerts for repeated failures against service accounts and for logons outside store hours, sent to the IT on-call number rather than a shared mailbox.
- Document every service account found, where it logs on and which store server uses it, then hand the list to the team for password rotation.
See it in ManageEngine ServiceDesk Plus
Real screens from the platforms we implement. Yours are configured to your entities, processes and KPIs.
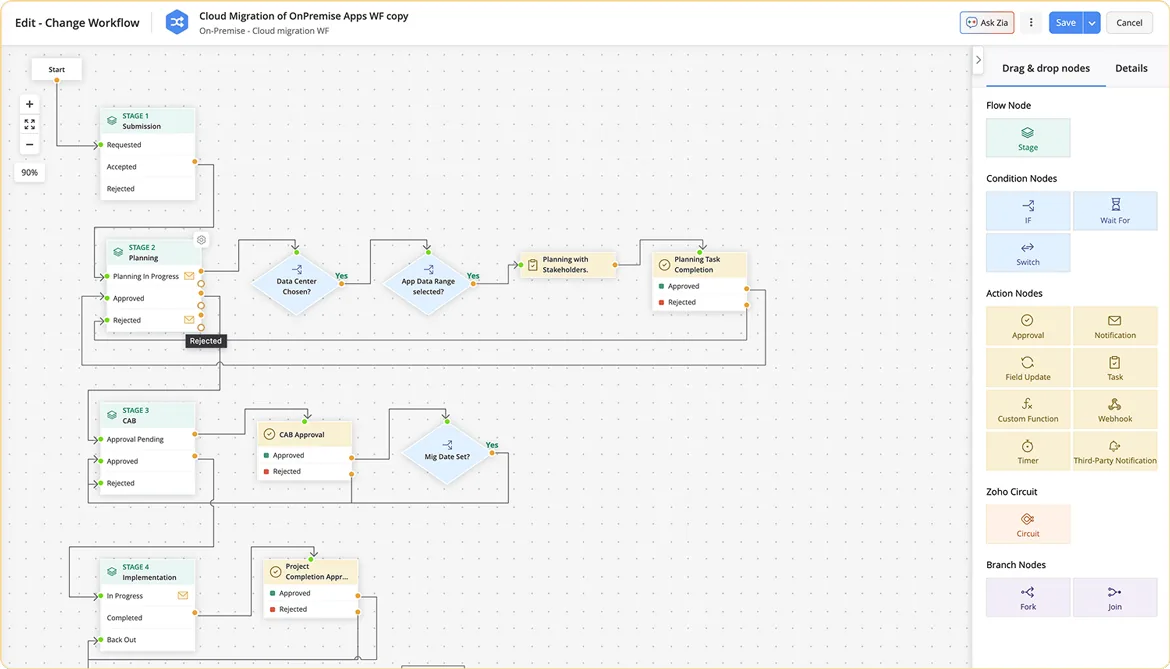
A change workflow in ServiceDesk Plus
A visual change workflow for a cloud migration, moving through submission, planning, CAB approval and implementation stages with conditions and approval nodes.
- AD change history
- File server access auditing
- Logon and lockout analysis
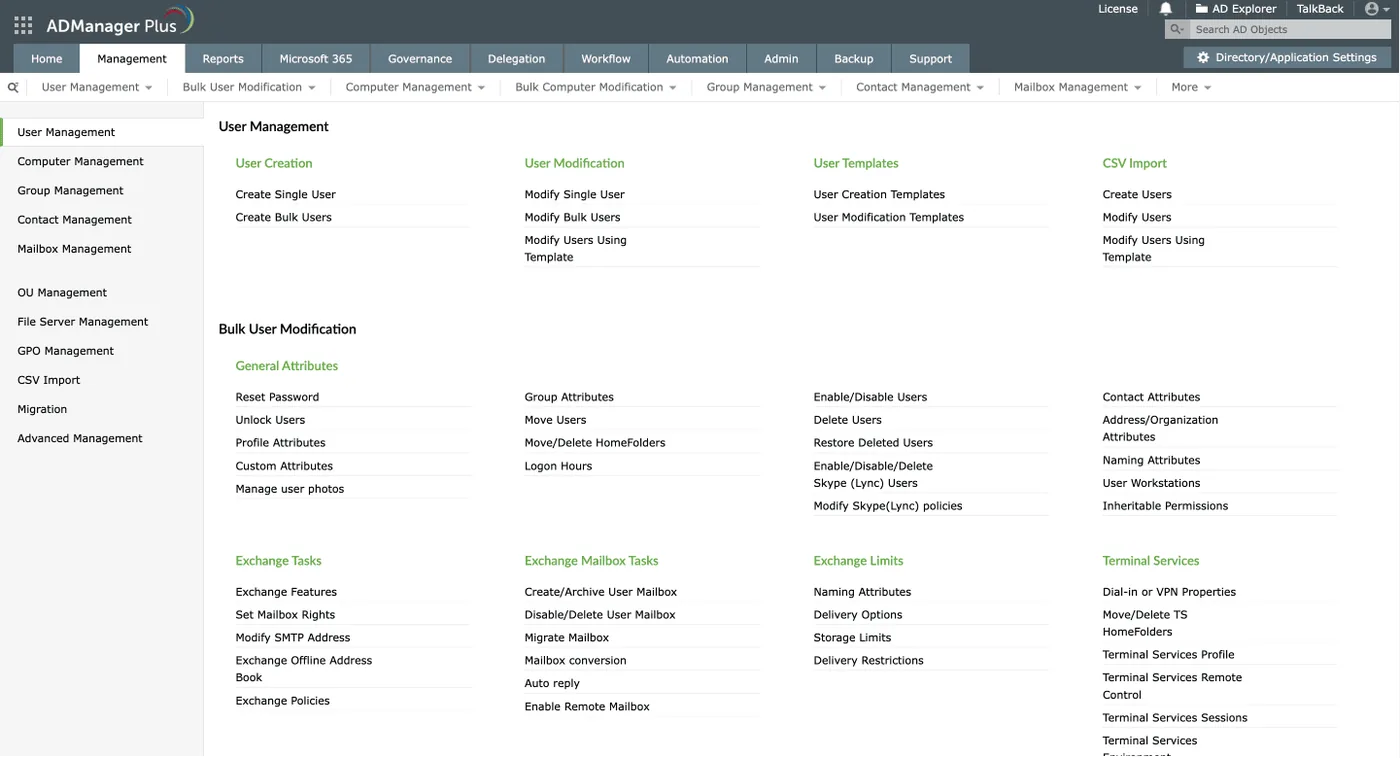
Active Directory user management in ADManager Plus
Single and bulk user creation, modification templates, CSV import and bulk tasks such as password resets, unlocks and Exchange mailbox changes.
- Alerts for risky changes
- PDPL, DIFC and ADGM evidence
- IA Regulation for critical sectors
 ServiceDesk Plus
 Endpoint Central
 PAM360
 OpManager
 ADManager Plus
 Log360
Which platform for manageengine adaudit plus implementation in the UAE?
An honest comparison. We implement all of these, so the recommendation follows your processes, team and budget.
| Option | Best when | How it fits this need |
|---|---|---|
| ADAudit Plus | You need clear answers on AD changes, logons and file access. | Well suited to UAE organisations with on-premises Active Directory and file servers that want ready-made reports and alerts, without building a security operations function first. |
| Log360 | Security staff need correlation across firewalls, cloud and servers. | A broader SIEM that includes ADAudit Plus features. Worth it when you have analysts to act on alerts across many sources; more than you need for AD and file questions alone. |
| Microsoft Defender for Identity | You hold Microsoft 365 E5 and want identity threat detection. | Strong at detecting identity attacks against AD. It is less focused on day-to-day change reports, file server access and auditor-friendly summaries, so some organisations run both. |
| Manual event log reviews | A handful of servers and no audit obligations. | Possible for a tiny network, but event logs overwrite quickly and cross-server searching is slow. It rarely produces evidence good enough for an investigation or external auditor. |
What changes in the UAE
The local rules and realities we design for before go-live. Rules change, so we re-check the current position at scoping.
PDPL, DIFC and ADGM evidence
Knowing who accessed personal data is central to the UAE PDPL and the DIFC and ADGM data protection laws. File access reports provide that evidence; we confirm the current requirement at scoping.
IA Regulation for critical sectors
Government-linked and critical-sector UAE entities working to the UAE IA Regulation need access monitoring and audit logging controls. ADAudit Plus covers the Windows and AD part of that.
Logs retained in the UAE
ADAudit Plus stores data on your own servers, so audit trails stay in your UAE data centre or UAE cloud region rather than a foreign SaaS.
What drives the cost, and what it connects to
No price list: we quote a fixed price in AED after discovery. These are the factors that move the effort up or down.
Domain controllers and servers
The number of domain controllers, file servers and member servers audited drives the licence and the number of audit policies we configure and test.
Workstation auditing
Adding workstation logon auditing across stores or branches widens coverage but increases event volume, licensing and tuning work, so we often phase it after servers.
Event volume and storage
Busy file servers produce large event volumes. Storage, archiving and database tuning grow with the data you keep and how long you keep it.
Reporting requirements
Standard reports need little work, while custom packs for auditors, HR, or a regulator, with schedules and recipients, need design and review time with each audience.
What it connects to
Change, logon and lockout events flow from every domain controller, with before and after values for attribute changes.
Cloud sign-in and directory changes are brought alongside on-premises events for organisations running hybrid identity.
High-priority alerts raise tickets automatically, and the ticket links back to the ADAudit Plus report used in the investigation.
When an audit shows an inactive or risky account, ADManager Plus can disable or clean it up through an approved workflow.
Selected events can be forwarded to an existing SIEM, so a security team keeps one place for correlation.
How we deliver manageengine adaudit plus implementation
Phases, indicative timing and what is delivered in each. Scope is fixed and priced in AED before we start.
Audit scope
Agree which domains, servers and shares to audit and what questions auditors usually ask. Confirm owners for each sensitive share.
Policy and sizing
Set advanced audit policies and SACLs, size the database and plan event retention. Test policy changes on one server first.
Deploy
Install, add domain controllers and file servers, and check event collection is complete. Add Microsoft Entra ID if you run a hybrid directory.
Alerts and reports
Configure alerts, report schedules and archives; test with simulated changes. Tune alert thresholds after a week of real events to cut noise.
Train and review
Train IT and compliance users and run a first access review together. Agree who reviews which report each month.
When manageengine adaudit plus implementation is the wrong answer
ADAudit Plus covers Windows and AD, not firewalls, Linux, databases or cloud apps. If you need one place to correlate logs from everything, Log360 (which includes ADAudit Plus) or another SIEM is the better buy. Buying ADAudit Plus alone and then a SIEM later can mean paying twice.
How we handle it: We implement Zoho, Odoo and Dynamics 365 and build AI and custom software, so our written recommendation can point you to a simpler option, or to doing nothing yet.
Checklist and common mistakes
Buyer's checklist
What to ask for before you choose a provider.
- Ask the provider to review your current Windows audit policy before installation, so events you need are actually being generated.
- Require a clear list of which domain controllers, servers and shares are in scope in the first phase.
- Check that lockout analysis will identify source devices, not just the affected user, and see an example.
- Ask how service accounts will be identified and documented as part of the project, not left as a separate task.
- Confirm the database sizing, retention period and archive plan in writing before any licence is purchased.
- Request a handover session where your team runs a real investigation from start to finish without help.
Common mistakes
What we see go wrong in the UAE, and how to avoid it.
- Installing before fixing audit policyADAudit Plus can only report events Windows generates. Review and set the audit policy through Group Policy first, or reports will be empty where you need them most.
- Ignoring service accountsService accounts with old passwords cause lockouts and hide real attacks. Use the project to list them, record their owners and plan password changes.
- One admin sees everythingGiving every technician full access to audit data weakens its value. Use roles so the people being audited cannot change reports or alerts about themselves.
- No test of restoreAudit data is only useful if it survives a server failure. Back up the ADAudit Plus database and test a restore before relying on it.
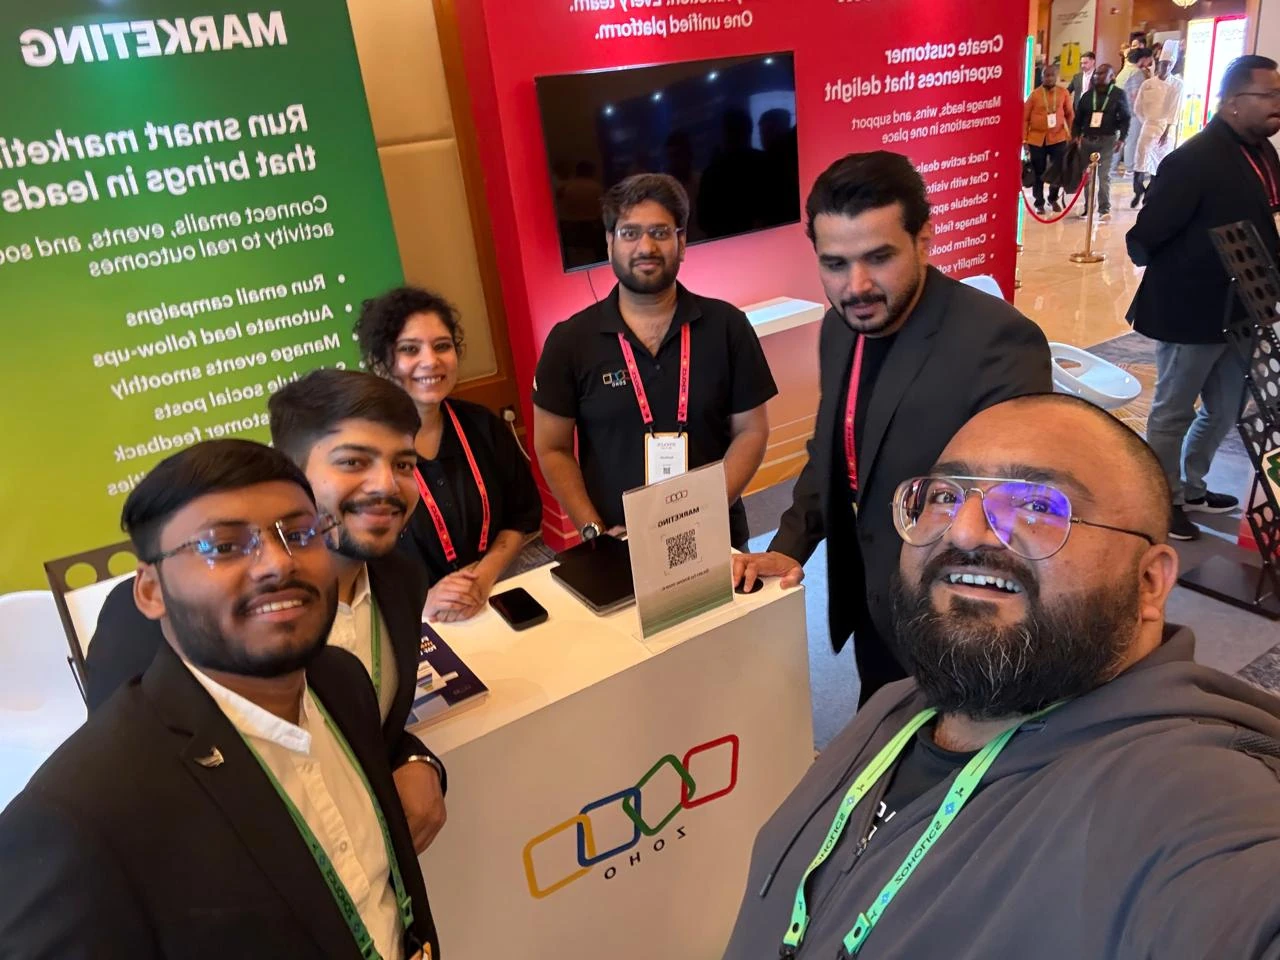
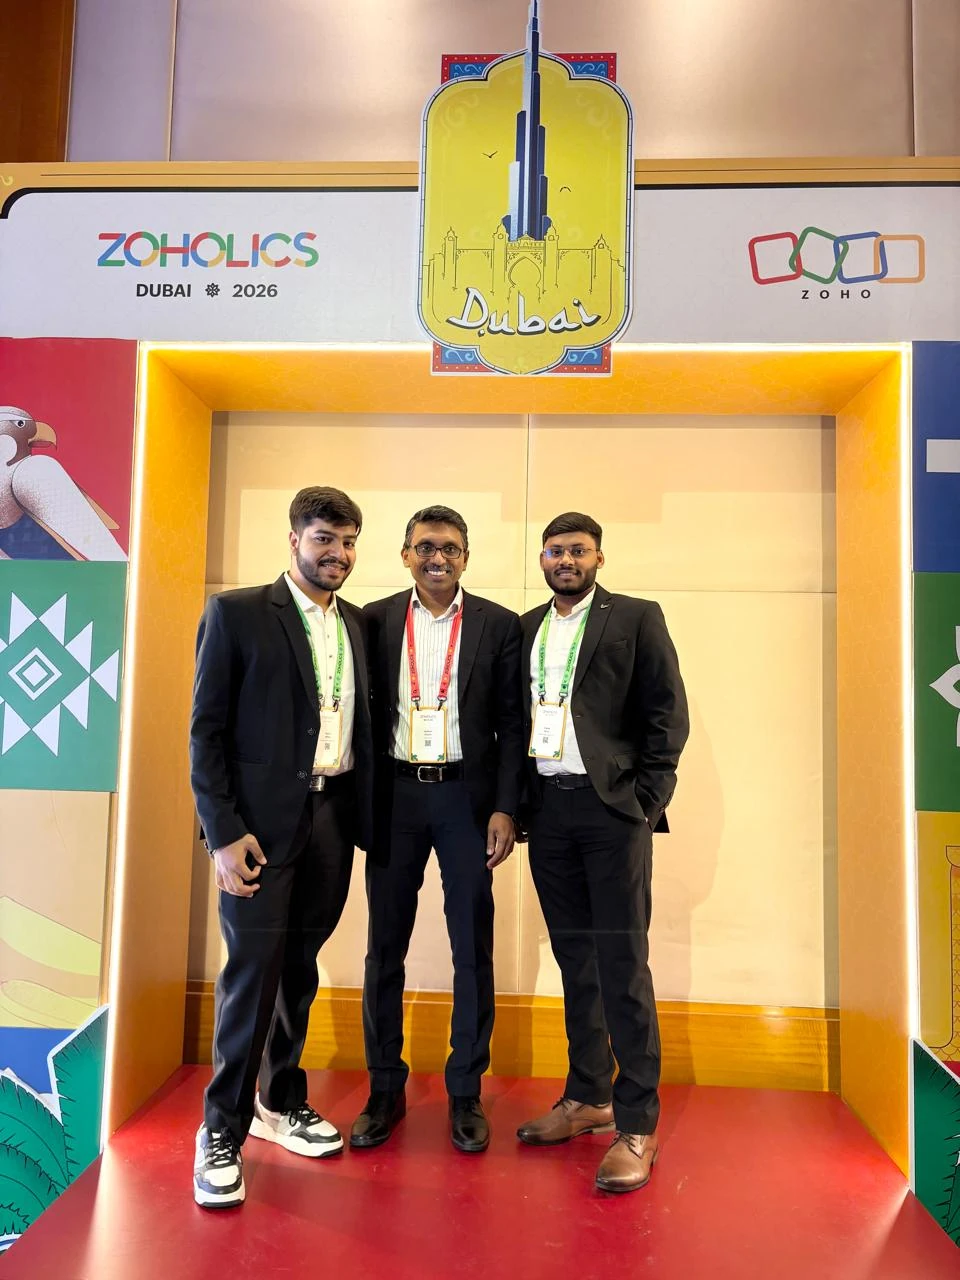
A UAE team you can meet in person
That is our team at Zoholics Dubai 2026. We deliver Zoho, Odoo, Dynamics 365 and custom projects from our Ras Al Khaimah office with remote delivery across all seven emirates, in English and Arabic, and we run workshops on site in Dubai, Abu Dhabi and Sharjah when a project needs it.
ManageEngine ADAudit Plus Implementation in the UAE: questions we get asked
What does ManageEngine ADAudit Plus UAE implementation cover?
How is ADAudit Plus different from ADManager Plus?
Should we buy ADAudit Plus or Log360?
Can ADAudit Plus detect ransomware on file shares?
Will auditing slow our domain controllers?
How long are audit logs kept?
Can ADAudit Plus find the device causing repeated account lockouts?
Does ADAudit Plus work with a hybrid Active Directory and Entra ID setup?
Which ADAudit Plus reports do UAE auditors usually ask for?
Why choose Shyphan?
Talk to a consultant about manageengine adaudit plus implementation
A free 30-minute call, then a written recommendation and a fixed quote in AED, including the honest option that this is not the right fit.